


Case Study
Komatsu Australia
How Komatsu Australia gained year-round visibility of SAP access risk with Soterion's Software as a Service.
The Komatsu Story
Komatsu Australia runs SAP with around 150 users. Soterion’s CEO, Dudley Cartwright, sat down with Shane Hubble of Komatsu Australia to talk about the company’s experience of moving to Soterion’s Software as a Service (SaaS) GRC tool.


Access Risk Results in a Spreadsheet
Before engaging Soterion, Komatsu relied on a service provider that sent its SAP access risk results in a spreadsheet. Navigating risk information this way was difficult, and the team had no ongoing access to the results between reports.
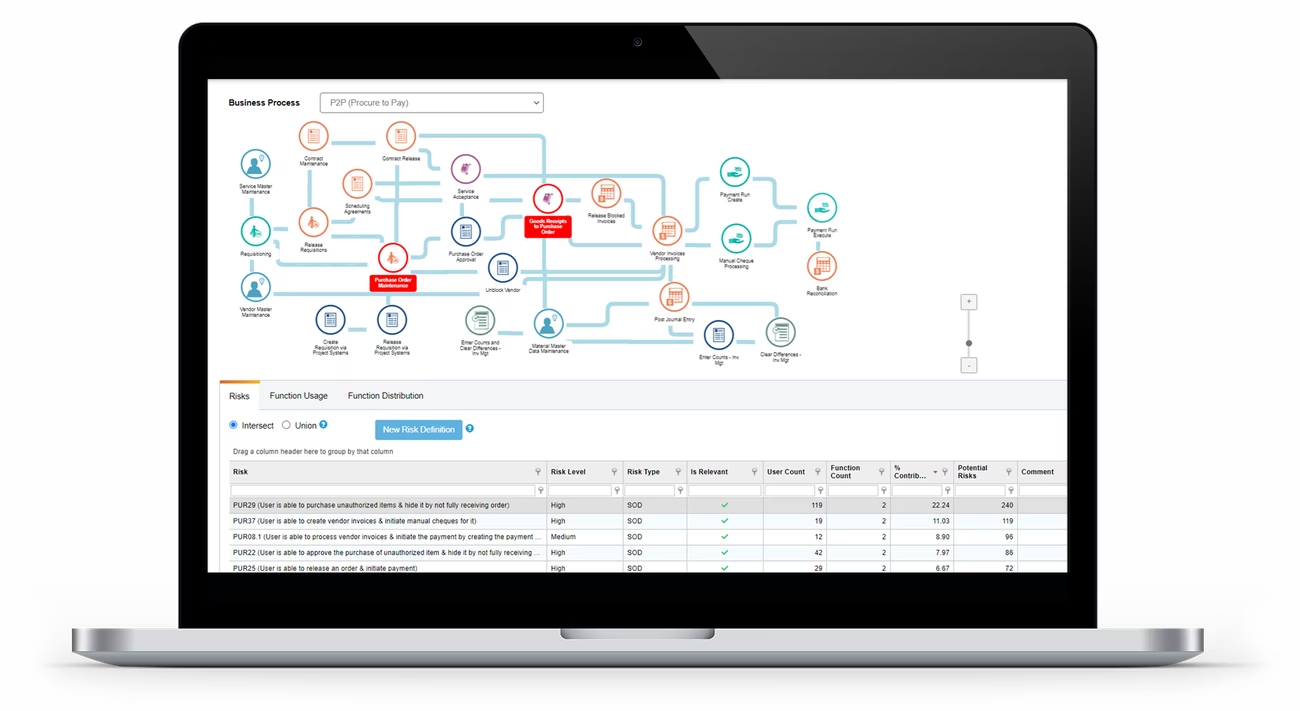
A Simple, Hosted Process
With Soterion, the process is simple. Komatsu uses the Soterion Data Extractor to extract the relevant data from SAP, and Soterion provides logon credentials for the hosted database. Results of each SAP access risk assessment are viewed in a user-friendly web application instead of a spreadsheet — and Komatsu has access to the application throughout the year.
Why Komatsu Chose Soterion

Komatsu imports its own risk rule set, focusing on risks relevant to the business and grading them by its own perceived risk levels.

Each user's risk violations are shown alongside whether the access has actually been used, so the team knows what can be removed without disruption.

User–transaction usage logs highlight superfluous access, so the security team can remediate it and focus on the real risk.

Risk assessments can be run on demand, at minimal cost.
“The Soterion process is so simple.”
Shane Hubble, Risk and Assurance Manager at Komatsu
Key Lessons from Komatsu's Implementation
- Spreadsheet-based reporting makes access risk hard to act on — a web application with year-round access gives the team the visibility it needs.
- Use a rule set that reflects your business, including risks specific to your environment, so reporting focuses on what matters.
- Combine risk results with transaction usage to remove access safely, without disrupting the business.
- Regular assessments drive improvement: after the first three, Komatsu saw enough improvement to reduce how often it runs them.

Each risk assessment plots a point on a historical trends graph, allowing Komatsu to monitor how its access risk has changed since previous assessments.

Komatsu started with a plan to run the risk assessment four times a year. After a huge improvement following the first three assessments, the team now feels it can reduce this to a couple of times a year.
Ready to take control of your SAP access risk?
Talk to a Soterion solutions expert.